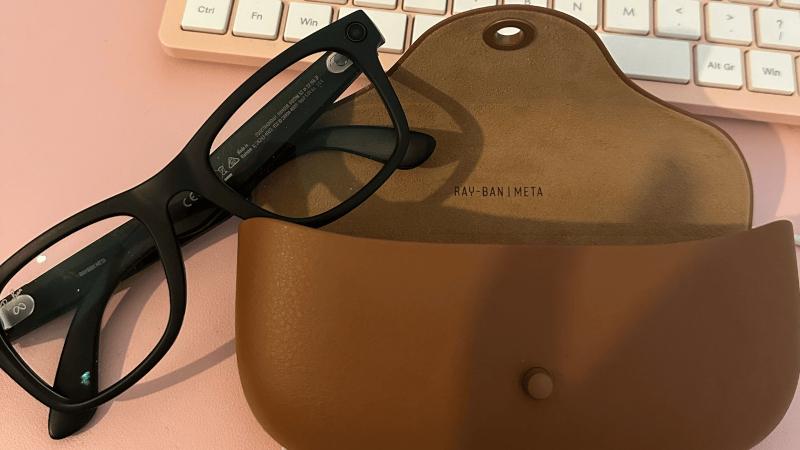
Meta's Ray-Ban smart glasses have drawn steady criticism since launch, mostly over fears that a camera hidden in everyday eyewear could enable covert recording. Now a security researcher has shown how the device itself could be opened up to run code it was never meant to run.
The researcher, who goes by p0pcycle, published a walkthrough of how she gained control of a pair of the glasses, according to a report by Hackaday. She later disclosed the issue to Meta through its bug bounty program.
Starting With Software Instead of Hardware
Physically tearing into the glasses was not an option, so p0pcycle focused on the software side. Her entry point was a software update, which she intercepted as it was delivered to the device.
By decompiling the companion app, she was able to locate and retrieve the complete firmware. That gave her a full copy of the code running on the glasses to examine at her own pace.
A Developer Mode With a Weak Spot
Inside the firmware she found a developer mode that lets people build applications for the glasses. Apps in this mode are delivered as an APK, the standard Android package format, which then loads the application code.
The key weakness was in an early firmware release, which accepted apps that were self-signed rather than verified by a trusted authority. That meant she could package her own code and have the glasses run it.
From Running Code to Opening a Door
Getting arbitrary code onto the device was only the first step. After some trial and error, she managed to set up a network listener on the glasses, giving her a way to communicate with the device remotely.
With that listener in place, she effectively had the access she was looking for, completing the chain from intercepted update to a working foothold on the hardware.
Disclosure and a Patched Firmware
Rather than releasing a working exploit, p0pcycle reported her findings through Meta's bug bounty program. As a result, the technique she described does not work on newer firmware versions.
Her write-up still serves as a detailed look at how the glasses are put together and where an early version fell short on verifying the code it trusted.
What It Means for Wearable Makers and Users
The episode highlights how much security in connected wearables depends on strict code-signing and on locking down developer features before they ship. A single permissive setting in early firmware was enough to open the device up.
For a product already under scrutiny over privacy, the outcome is a reminder that independent researchers and bug bounty programs play a real role in hardening consumer hardware. Further probing of the glasses by others seems likely.
Source: Hackaday